
UIC Interoperability Standards: What Rail Signaling Teams Must Verify

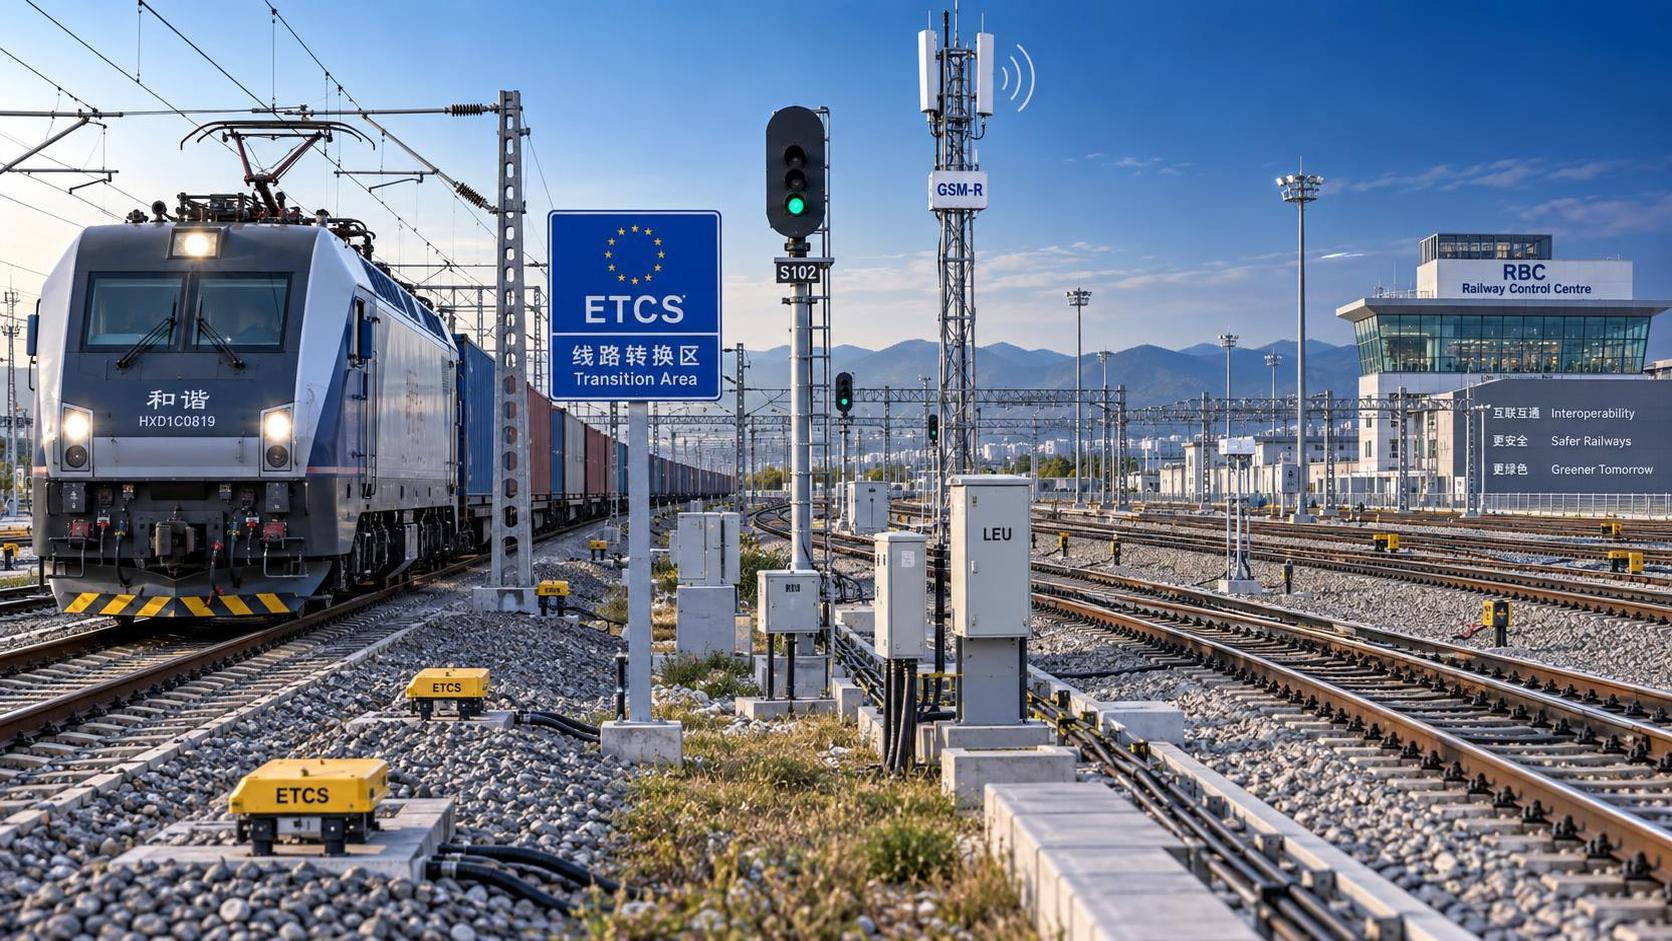
UIC interoperability standards should be treated as an evidence-based compatibility question, not a document-matching exercise. A signaling installation can use familiar equipment, carry the expected approvals, and still fail to interoperate at a corridor boundary because its operational assumptions differ from those of the adjacent network. The verification target is the complete safety-relevant chain: trainborne equipment, trackside equipment, radio bearer, traffic-management interfaces, configuration data, operating rules, and maintenance controls.
For cross-border freight routes and mixed-technology networks, the most serious defects often appear at transitions rather than within a single subsystem. A train may establish a radio session but receive an incompatible movement authority format. A balise group may be physically correct yet reference configuration data that does not match the onboard baseline. A route may work during normal operation but enter a restrictive or unsafe degraded mode when a communication session is lost. UIC interoperability standards provide a common frame for examining these relationships, while the applicable national, infrastructure, and project requirements define the precise technical acceptance conditions.
Start with the operational boundary
Interoperability must be assessed against an explicit operational scenario. “Compatible with ETCS” is too broad to support acceptance. The review should identify the ETCS level or levels in use, the permitted transition paths, train categories, braking regimes, radio coverage model, route speeds, axle-load constraints where they affect braking assumptions, and interfaces with legacy protection systems. A freight locomotive crossing from a conventional national protection zone into an ETCS-controlled section faces a different verification problem from a passenger unit operating only inside a continuous Level 2 area.
Boundary definition should include both geographic and functional limits. Geographic limits cover border stations, terminals, tunnels, yards, radio cells, and changeover areas. Functional limits cover system-version changes, transitions between supervision modes, handover between radio network elements, changes in train data responsibility, and movement from mainline operation into depot or shunting conditions. A boundary need not coincide with a national border. A revised interlocking interface, a new radio core, or a local speed-profile rule can create an equally important interoperability boundary.
Each claimed route should therefore be accompanied by a route-specific compatibility statement. It needs to state the onboard software and hardware configuration, relevant trackside release, communication profile, configuration-data version, and permitted operational modes. General product declarations cannot replace this route-level evidence.
Interfaces must be verified as behavior, not labels
Interface control documents are necessary, but their presence does not prove that two systems exchange information correctly under all relevant states. The review should trace the data path from route setting through the interlocking and radio-block interface to the trainborne supervision function. At every handoff, confirm the message source, permitted value range, timing expectation, integrity protection, acknowledgement behavior, and response to invalid or unavailable data.
A common error is to assess a communications interface only at the packet or protocol level. Correct packet framing, addressing, and session establishment do not demonstrate that the operational meaning is consistent. For example, a movement authority can be syntactically valid while containing a speed, gradient, route, or end-of-authority interpretation that conflicts with onboard configuration data. The evidence should connect message-level tests to the resulting trainborne state, displayed information, braking-curve calculation, and any safety reaction.
ETCS compatibility is a configuration problem as well as a product problem
ETCS interoperability depends heavily on the exact combination of onboard and trackside versions, national values, data sets, and engineering rules. It should not be inferred from the presence of ETCS equipment alone. The review needs a controlled configuration matrix that identifies every safety-relevant software release, parameter set, national value set, data-preparation tool version, and baseline relationship used on the intended route.
National values deserve particular scrutiny because they can influence supervision behavior without being obvious in a high-level system description. Values related to braking, release speed, train categories, mode transitions, or operational timing need to be checked against the route engineering assumptions and the onboard implementation. A valid national-value packet is not enough; its effect must be demonstrated in the relevant train configuration. Differences between freight and passenger braking performance make this especially important. A parameter set validated with a short, high-braked train does not automatically represent a long freight consist with different brake build-up behavior and permitted speed conditions.
Trackside data quality must be evaluated as a lifecycle-controlled asset. This includes the chain from route design to data preparation, independent verification where required, loading, installation, commissioning, and subsequent change control. The critical question is whether a maintainer can prove that the telegram or radio data in service is the approved data for that physical location and route state. Asset identifiers, version records, installation drawings, and test results should resolve to the same controlled baseline. Any break in that chain creates a latent interoperability risk, especially after phased resignalling or partial corridor upgrades.
Transitions require dedicated test cases
Mode and level transitions should be tested in the direction, train state, and communication state in which they will actually occur. A transition demonstrated with a stationary test vehicle or an empty train may miss timing effects associated with speed, braking demand, train length, or radio handover. Tests should include successful transition, delayed confirmation, missing transition information, repeated information, and an interruption near the transition point. The expected outcome must include the indicated mode, permitted traction behavior, braking response, driver acknowledgement where applicable, and conditions for recovery.
Mixed fleets add a further distinction. Two onboard units can claim the same functional level yet respond differently because of software release, optional functionality, configuration, or implementation constraints. Compatibility assessment should identify the minimum supported onboard population, not merely a representative vehicle. Where a route relies on a particular onboard behavior, that dependency needs to be visible in the operating and change-management records.
GSM-R and radio resilience need an end-to-end view
For systems using GSM-R, verification extends beyond radio coverage maps. The safety-relevant concern is whether the train can maintain or restore the communications relationship required by the operational concept. This involves network registration, call or data-session establishment, addressing, authentication where implemented, cell reselection, handover behavior, congestion response, and recovery after an interruption. Coverage can appear adequate while session continuity is poor at a border area, tunnel portal, terminal approach, or network handover point.
Radio testing should distinguish between a weak signal, a lost session, an unavailable network element, delayed message delivery, and an addressing or configuration error. These conditions may produce similar symptoms on the train, but they demand different corrective action. Treating them as a generic “GSM-R failure” can mask a defect in the radio network, onboard configuration, control-center interface, or operational procedure.
The review should also examine what happens after communications degrade. A safe response is not automatically an efficient response, and an efficient-looking recovery is not automatically safe. Confirm the imposed supervision state, authority limits, timer behavior, permitted movement, re-establishment conditions, and event recording. Where fallback procedures require manual intervention or a transition to another protection system, the procedure must align with the actual route equipment and trainborne capability. The timing and authority of any manual action must be unambiguous.
Fail-safe claims need observable failure evidence
Fail-safe design is often described in broad terms, yet acceptance requires specific failure hypotheses. The relevant question is not whether the system “fails safe” in principle. It is whether each credible interface failure leads to a defined, detectable, and controlled state without producing conflicting information or bypassing a safety function.
- A stale route-status message should be differentiated from a message that fails integrity validation. One concerns the age and validity of information; the other concerns trust in the message itself. Their system responses may be deliberately different.
- Loss of a balise telegram, an unreadable telegram, and a telegram with valid coding but incorrect route data should not be collapsed into one field-test condition. Each affects onboard processing differently.
- Redundant components need proof of failure detection and switchover behavior. Redundancy that transfers a latent configuration defect, an outdated data set, or a common power fault provides limited protection.
- Reset and restart behavior deserves the same attention as initial operation. After a power interruption, software restart, or maintenance intervention, confirm which state is restored, which data must be reacquired, and which movement remains prohibited until verification is complete.
Fault injection, simulation, and controlled field testing all have a place, but they are not interchangeable. Simulation is useful for rare message sequences and broad state coverage. Field tests establish timing, radio, installation, and electromagnetic conditions that models may not fully reproduce. Test evidence should state which environment generated the result and which assumptions remain outside its scope.
Lifecycle evidence determines whether compliance survives change
Interoperability can degrade after commissioning when one side of an interface changes without a coordinated assessment. Software patches, renewed radio equipment, revised interlocking logic, altered national values, new rolling-stock brake data, and route extensions can all change behavior. The original acceptance dossier is therefore a starting point, not permanent proof.
A controlled change process should identify affected interfaces before implementation, assess the impact on safety and operations, define regression tests, and retain the configuration state before and after the change. The strongest records connect change requests, hazard assessments, test specifications, test logs, anomaly disposition, and released configuration baselines. A list of closed defects without this linkage does not establish that all affected operational scenarios were retested.
Traceability matters most when documents disagree. A test report may reference an engineering version that no longer appears on site; a radio parameter sheet may use a route identifier different from the control-center configuration; a vehicle log may record a software identifier not reflected in fleet records. These discrepancies should be resolved as configuration questions, not dismissed as administrative errors. In rail signaling, an administrative mismatch often reveals an untested interface or an uncontrolled deployment step.
Acceptance evidence should expose limitations
Clear interoperability evidence states both the demonstrated capability and its boundaries. It identifies supported routes, train configurations, transition conditions, operational modes, known restrictions, and dependencies on external systems. Ambiguous claims such as “interoperable,” “ready for cross-border use,” or “compliant with UIC requirements” do not show whether the system has been tested against the operational conditions that matter on a particular corridor.
Before release, the evidence set should allow a reviewer to reconstruct a complete story: the applicable requirements, the controlled design, the installed configuration, the tests performed, the failures observed, the decisions taken, and the conditions under which the result remains valid. When that story cannot be reconstructed, the remaining issue is not merely missing paperwork. It is uncertainty about whether the signaling system will behave predictably when the route, vehicle, radio network, or operating state changes at the point where interoperability is most exposed.
Industry Briefing
Get the top 5 industry headlines delivered to your inbox every morning.